

Audit logs are available on Enterprise plans. Contact us to enable audit logs for your organization.
What’s tracked
Audit logs capture security-related events and administrative changes, including:- Authentication — successful and failed logins, logouts, and session management
- Passwords & MFA — password resets, changes, MFA setup and removal
- API keys — enabling, regenerating, and revoking API access
- User management — inviting, disabling, and changing roles for team members
- Groups — creating, renaming, and modifying group membership and access
- Organization settings — name changes, MFA requirements, and org deletion
- OAuth apps — creating, deleting, and resetting secrets for developer apps
Viewing audit logs
Go to Settings → Audit logs in the left sidebar. You’ll see a table of recent events with:- Time — hover for the exact timestamp
- Performed by — who performed the action and their role
- Action — the event type (e.g.,
auth.login.success,user.invite) - Resource — what was affected
- Outcome — whether it succeeded or failed
Filtering
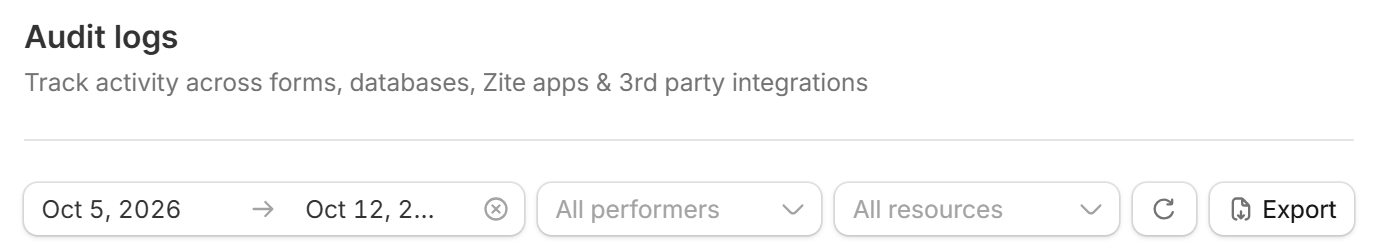
Use the filter bar at the top of the page to narrow events by:- Date range — select a start and end date
- Performers — open
All performersto filter by Org members, API keys, or Unknown - Resources — open
All resourcesto filter by Users, Tables, Fields, Views, Databases, Forms, Apps, Organization, or Groups
Exporting
To export your audit logs, go to Settings → Audit logs and clickExport next to the filters. You can export as CSV or JSON.
- CSV - opens in any spreadsheet tool. Values that a spreadsheet could read as a formula start with an apostrophe, so they aren’t run as formulas.
- JSON - keeps every value exactly as recorded.
Event categories
Events are organized into these categories:
For a complete list of every event type and what data is captured, see the event types reference.